Is Anonymous Visitor Identification Legal Under UK GDPR and PECR?
It can be, but two separate questions have to be answered, and many tools only answer one of them. The first is whether the visitor agreed to a tag reading information about their visit. The second is whether the person identified has agreed to receive marketing email from whoever sends it. A tool can get the first right and still fail the second, and the reverse is also true.
What does the law require for the identification step?
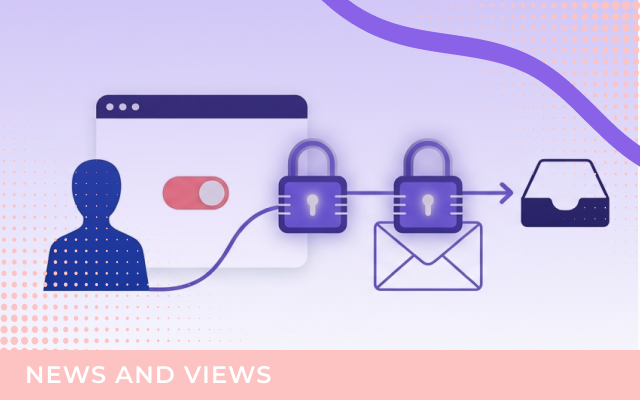
Anonymous visitor identification starts with a small piece of code on a website, called a tag, reading technical information about a visit, such as IP address, device and browser details. Under UK GDPR, that needs the visitor’s consent. In practice the consent is captured on the website’s own cookie banner, known as a consent management platform (CMP): the visitor has to accept marketing consent there before the tag reads anything about them. If they decline, nothing is read and no identification takes place. PECR regulation 6, which covers reading information from a person’s device, adopts the same UK GDPR standard of consent (freely given, specific, informed and unambiguous), so a single valid consent on the CMP covers both.
What does the law require for the email step?
PECR regulation 22 requires a specific legal basis, normally consent, or in narrow circumstances the “soft opt-in”, before sending marketing email to an individual. UK GDPR applies alongside it, because an email address is personal data. The key question is who holds that consent and whether it genuinely covers the email being sent. Optivo’s emails are sent by esbconnect as sender of record. Every consumer in the database has opted in to receive marketing email through opt-me-in.com, where they are shown the types of email they will receive and the brands esbconnect works with, During their welcome journey they also receive an email dedicated to Optivo, explaining what it does and the value it brings them. They can opt out at any point.
How does the process work, step by step?
- Optivo’s tag is placed on the brand’s website.
- A visitor accepts marketing consent on the brand’s own cookie banner (the CMP).
- With that consent in place, the tag reads technical information about the visit, such as IP address, device and browser details, and matches it against the 17 million consumers in the esbconnect email community.
- If there is a match, and the person is not on the brand’s suppression file, Optivo emails them under the explicit consent they already hold to receive marketing email.
- The email invites them back to the site to buy, or to opt in to the brand in a single click. They receive up to three emails unless they purchase or opt in to the brand directly.
- Only if they opt in does the brand receive their details, for example through an API connection to its CRM or customer data platform.
What happens when the consent chain breaks?
The ICO’s enforcement record shows what failure looks like. In an enforcement notice dated 20 January 2026, the ICO fined ZMLUK Limited £105,000 for breaching PECR regulation 22. ZMLUK had sourced marketing data from a third-party website that presented people with a list of 361 “partner” companies and no way to choose which of them could contact them. The ICO found that people “could not give informed, specific consent, rendering the consent invalid”, and that ZMLUK had sent 67.7 million marketing emails between January and July 2023 without valid consent, having relied on third-party data without checking how that consent was obtained. Read the ICO’s announcement for the full detail.
The pattern is an intermediary relying on someone else’s consent without verifying it holds up at the point the email is sent. Anonymous visitor identification is not unlawful in itself. The risk comes from how the consent chain is built.
How active is enforcement?
An analysis of ICO enforcement in 2025 found six PECR-related fines and notices, totalling £1.025 million, none reaching the £500,000 statutory maximum. That is a smaller share of total enforcement than in 2024, but it shows PECR is still being actively enforced.
How does the sender-of-record model differ from a list-handoff model?
What matters most is who holds the matched identity and who sends the email.
| Model | Who holds the matched identity | Who sends the email | Where consent must hold up |
|---|---|---|---|
| List-handoff model | The brand | The brand, using a third-party-sourced list | At collection, by a party the brand did not control |
| Sender-of-record model (Optivo) | esbconnect, in its opted-in database | esbconnect, under its own consent chain | At the cookie banner for identification (UK GDPR), and in the opt-me-in.com sign-up for email (PECR and UK GDPR) |
In the sender-of-record model, the brand never receives matched personal data. The brand does not receive a list of identified visitors. A person only becomes a contact in the brand’s CRM if they choose to opt in to that brand from an Optivo email, and only then is their email address passed on, for example through an API connection. This removes the failure seen in the ZMLUK case, where the brand holding the list was also responsible for verifying consent it could not see.
What should a DPO check before switching this on?
Before approving any anonymous visitor identification tool, confirm in writing: how a visitor’s consent is captured on your own cookie banner before the tag reads anything, who holds the consent to email the person identified, who the sender of record is, and whether your business ever receives matched personal data before the person has opted in. The ICO’s guidance on cookies and similar technologies sets out the consent standard for the first of those checks and is the right starting point.
Next step: Ask us to walk your DPO through Optivo’s consent chain.
More News & Views


Sign Up Today
Want to keep on top of all things from Optivo, including news, thought pieces, white papers, and product releases?
By clicking Sign Up you're confirming that you agree with our Terms and Conditions
